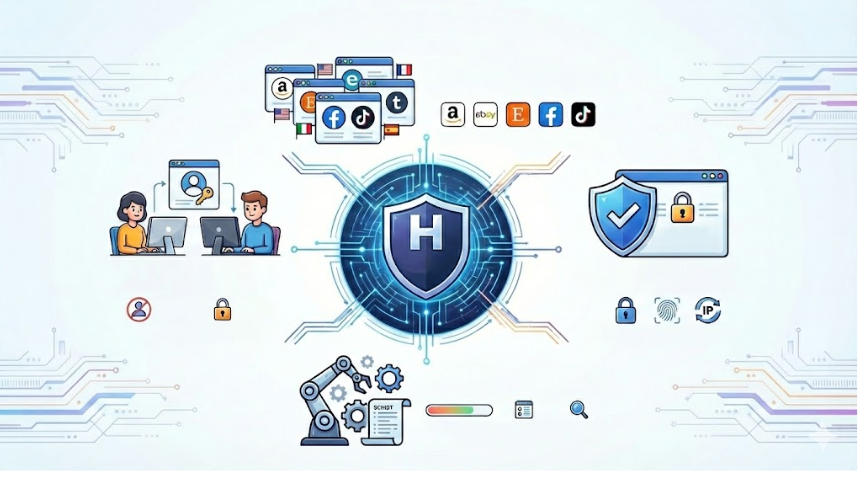

To manage multiple authorized online accounts more consistently, create a dedicated browser profile for each work context, label profiles by client and platform, keep session data separate, configure network settings where required, and grant teammates only the access they need. Hidemium can organize these browser environments in one workspace. It cannot guarantee immunity from account reviews, checkpoints, restrictions, or bans. Platform policies and legitimate account ownership still matter.
1. Why Does Multi-Account Management Become Difficult at Scale?
A team working across Facebook Ads, Google services, marketplaces, and TikTok may have dozens of authorized client accounts. The practical problem is not simply the number of logins: it is maintaining a clear relationship between each account, its owner, its working environment, and the employee responsible for it.
1.1 Shared sessions, cookies, and browser configuration
Traditional browser windows can lead to accidental account switching or session confusion if profiles are not organized. Websites may assess network information, browser properties, cookies, authentication history, payment relationships, and behavioral signals. Browser fingerprints can include User-Agent, Canvas, WebGL, fonts, language, and screen characteristics, but platforms do not publicly disclose every detection rule. Read how browser identities and fingerprints work for background.
1.2 Unstable access and inconsistent operations
Frequent logins from unfamiliar locations or unusual account activity can create extra authentication work. However, an IP address or matching fingerprint alone does not establish that an account will be suspended. Reviews also depend on platform rules, account history, content, identity, and commercial activity.
1.3 Team permissions and accountability
Unstructured password sharing, unclear ownership, and overlapping staff responsibilities can expose client assets. A sound multi-account process needs role ownership, access reviews, two-factor authentication (2FA), and a documented handover procedure.

2. What Does Hidemium Help You Manage?
Hidemium is an antidetect browser offering separate browser profiles and configurable fingerprint and proxy options. Its main operational value is helping teams maintain distinct browser workspaces rather than juggling unrelated sessions in one window. See what Hidemium is and how antidetect browsers work.
Capability | Practical purpose | Important limitation |
| Separate browser profiles | Keep profile cookies and local session data apart | Does not erase relationships through payment, ownership, or platform records |
| Fingerprint configuration | Set a consistent browser environment for each workflow | Does not make an account invisible or automatically legitimate |
| Per-profile proxies | Configure a chosen network connection where needed | Proxy quality and account rules still matter |
| Groups and labels | Sort work by client, platform, and campaign | Needs a naming convention and periodic cleanup |
| Team collaboration | Delegate available profile access within plan capabilities | Verify roles and permissions in your current Hidemium plan |
| Automation integrations | Reduce repetitive approved administrative tasks | Must comply with each platform's automation rules |
2.1 One profile per work context, not one false identity per account
Create profiles based on legitimate operating needs: an agency's authorized client workspace, a specific marketplace business, or a testing environment. Keep each profile associated with its actual account owner. Profile isolation helps separate browser data but cannot guarantee that platforms will treat profiles as unrelated individuals.
2.2 Centralized organization and collaboration
A useful naming template is Client_Platform_Role_Owner_Region, for example NorthCo_MetaAds_Reporting_Lan_US. Use shared folders or groups where supported, document who owns each profile, and remove access when a staff member changes roles. Use official platform delegation tools whenever possible instead of distributing passwords.

3. How to Set Up a Multi-Account Workflow in Hidemium: 7 Steps
Step 1: Inventory your accounts and check platform rules
List the account owner, platform, business purpose, current access method, staff responsible, and verification requirements. Confirm whether the platform allows multiple accounts and whether client delegation is available. Do not create duplicate accounts to circumvent a restriction.
Step 2: Group profiles by client and workflow
Use a consistent directory or group structure. Separate advertising, marketplace operations, support, and test workspaces, while recording the real owner of each account. Do not copy sensitive session files between unrelated clients.
Step 3: Create and label a browser profile
In Hidemium, create a new profile, apply an understandable name, choose the relevant browser settings, and save it. The exact button names may vary by version. Avoid random changes to settings during an established work session.
Step 4: Configure a proxy only when operationally justified
If a particular workflow requires a stable network region or dedicated connection, choose an authorized provider, enter proxy settings, and record their owner and renewal date. Different proxy types have different performance and costs; there is no universal requirement for one proxy per account. Read how antidetect browsers and proxies work together.
Step 5: Verify the actual browser and network signals
Open the profile and check the outgoing IP, time zone, language, WebRTC, and DNS using suitable testing pages. Confirm expected values before business-critical use. Follow Hidemium's IP and fingerprint checking guide.
Step 6: Apply access controls and authentication
Use platform-native business permissions, 2FA, least-privilege access, and documented approval for sensitive changes. If using Hidemium's team features, confirm available roles in your subscription. Do not assume that profile sharing replaces the platform's permission system.
Step 7: Run a routine operational review
Review profile naming, unused profiles, proxy renewal, failed logins, staff permissions, and policy notifications weekly. Record changes in a simple tracking sheet. Automate only permitted tasks, such as approved internal reporting or QA checks.
4. Example Management Structure for Agencies and E-commerce Teams
Business use | Suggested profile grouping | Primary control |
| Facebook/Meta Ads | Client → ad operations → staff | Official Meta role-based access and 2FA |
| Google services | Client → service → owner | Google account and organization permissions |
| Amazon/eBay stores | Store → operations → support | Seller-policy compliance and authorized access |
| TikTok marketing | Client → campaign → operator | Approved business access and platform rules |
| QA and automation | Test project → environment | Test data and documented automation scope |
For a platform-specific example, see Hidemium's Facebook Ads team-management guide and the comparison of standard and antidetect browsers for Ads workflows.
5. What Benefits Can You Realistically Expect?
Less session confusion: clear profiles and labels reduce accidental logins to the wrong client workspace. Better handovers: documented ownership and permissions make onboarding and offboarding more manageable. Repeatable setup: agreed templates reduce unnecessary configuration differences. Clearer audits: teams can identify which environment was used, which settings changed, and who is responsible.
These are operational benefits, not verified promises of a 70% reduction in labor or a guaranteed improvement in account approval rates. Measure your own results with onboarding time, login-related incidents, number of outdated permissions, and time spent resolving access issues.
6. Common Mistakes and Troubleshooting
Problem | What to check | Recommended action |
| Unexpected verification prompt | Official security notice, location history, login owner | Complete verification through the platform; avoid repeated automated logins |
| Wrong account opens | Profile label, selected client, existing session | Pause work, check owner, correct naming |
| Proxy works but location differs | Actual outgoing IP, DNS, WebRTC, proxy rotation | Re-test from inside the profile and contact provider if needed |
| Staff lose access | Hidemium role, subscription, platform-native permissions | Check both permission layers and restore only authorized access |
| Account is restricted | Platform policy notice, billing, business verification | Follow official review/appeal instructions; do not bypass a restriction |
See common account-management risks and prevention principles for additional context.
7. Pre-Launch Checklist
- Every account has a documented legitimate owner and purpose.
- Multi-account use is consistent with each platform's rules.
- Profiles follow a consistent naming and grouping scheme.
- Session data is kept in its intended profile.
- Proxy and browser settings have been verified when applicable.
- 2FA and official team permissions are enabled.
- Former employees no longer have unnecessary access.
- A review and incident-response owner is assigned.
8. Conclusion
Managing multiple online accounts efficiently depends on clear ownership, separated working sessions, secure permissions, and consistent team procedures. Hidemium can provide a central browser-profile workspace for these tasks, but no antidetect browser can guarantee that accounts will escape policy enforcement or verification.
Build a process that can be audited, measured, and maintained. Explore Hidemium's available features and verify the tools included in your current plan before scaling.
9. Frequently Asked Questions
Can Hidemium prevent all account bans?
No. It helps organize isolated browser environments, but decisions about restrictions and suspensions remain with each platform.
Can one computer manage many profiles?
Yes, subject to device resources and your subscription's profile limits. Running many profiles simultaneously can affect performance.
Does every profile need a different proxy?
Not necessarily. Choose network settings based on legitimate requirements, stability, budget, and platform rules.
Are browser profiles the same as physical computers?
No. They are software environments that can separate browser data and present configurable browser characteristics, not fully independent hardware devices.
Can teams share profiles without sharing passwords?
Hidemium offers team-related features, but the exact permissions depend on the product version and plan. Prefer official platform delegation wherever available.
Does isolation remove all account connections?
No. Platforms may use billing information, business ownership, identity, session history, and other signals.
Will Hidemium increase an account's trust score?
There is no evidence of a universal platform trust-score improvement attributable to Hidemium. Follow platform rules and legitimate security processes.
Is automation safe for all sites?
No. Review the relevant platform's automation rules and only automate permitted workflows.
What should I do if a profile fails its IP test?
Check the configured proxy, test within the correct profile, and review WebRTC/DNS results before using the profile.
Is Hidemium suitable for agencies?
It can be useful where teams need consistent browser profiles, clear labels, and managed access, alongside official business-account permission systems.
.png)